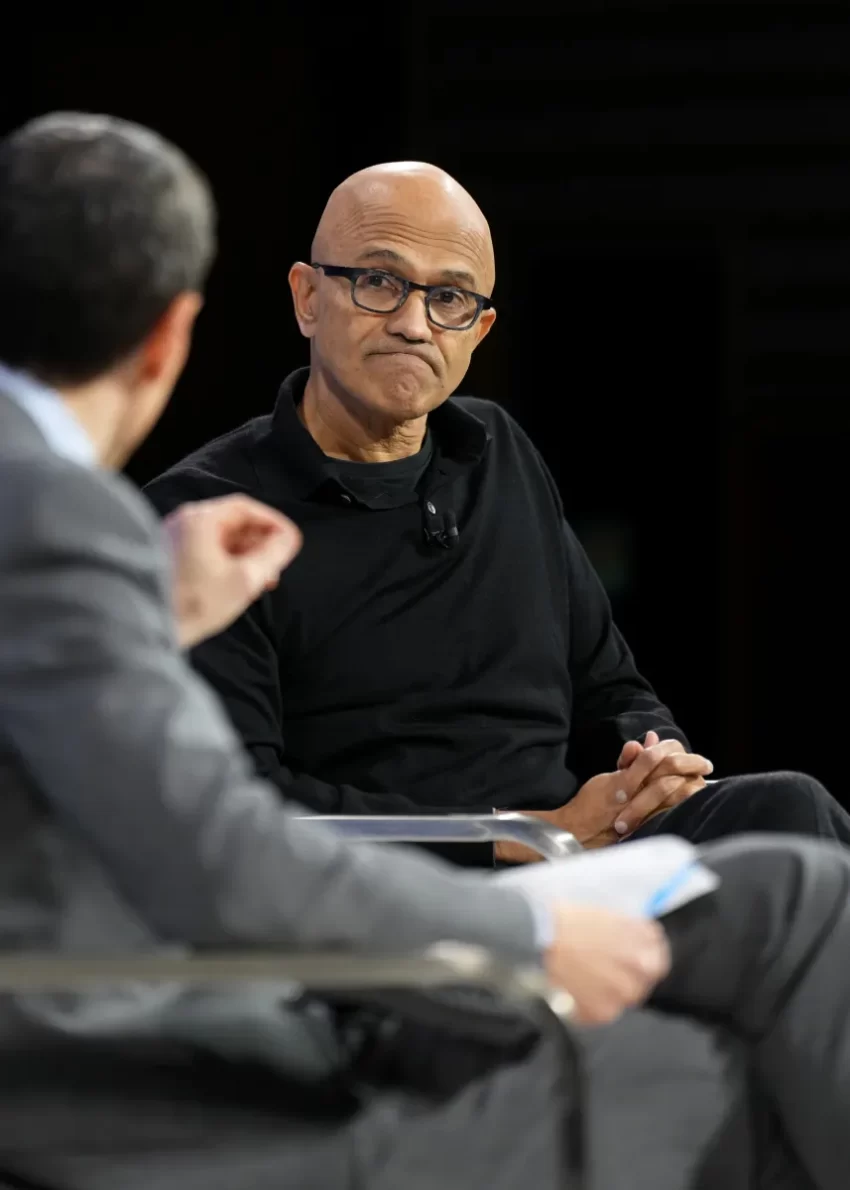
Microsoft CEO Satya Nadella used a New York Times DealBook Summit appearance to warn that a large amount of critical infrastructure is still vulnerable in ways that modern security practices cannot easily fix. In the era of AI-aided cyberattacks, he argued, that leaves many everyday systems exposed to threats that can be discovered faster than they can be patched.
Satya Nadella on the problem of unpatchable infrastructure
Speaking on Wednesday at the summit, Nadella said many of America’s software systems — including the ones behind basic hardware and transportation services — have vulnerabilities that cannot simply be eliminated with a routine update. He described parts of the internet-connected world as effectively “unpatchable,” pointing to the growing security burden created by the spread of connected devices.
“Remember, there is a lot of stuff in our critical infrastructure that’s unpatchable,” Nadella said. “I mean, think about all the firmware and the chillers [a cooling device often used in data centers] and the HVAC systems everywhere else. So all of that, by the way, they’re on the internet.”
His comments reflect a broader concern: devices once considered isolated or “dumb” are now networked, monitored and remotely managed, but not always designed for easy security maintenance. That makes them a tempting target when attackers can use AI tools to search for weaknesses at scale.
Why AI cyberattacks raise the stakes
Nadella framed the issue as part of a larger shift in the balance between defenders and attackers. The tools used to find vulnerabilities have become more powerful, while the time available to evaluate and deploy fixes has become shorter. That combination, he suggested, is creating a more unstable security environment.
“We now have a very powerful tool that finds vulnerabilities,” he said. In earlier eras, companies had more time to test patches, understand the impact of a flaw, and roll out repairs. Now, he said, attackers can exploit weaknesses much faster, forcing defenders into a race to respond.
“The patch [now] needs to go instantly from being available to being patched in production, because it’s being exploited in the wild, right? So that’s going to create instability,” Nadella said.
That warning is especially relevant for critical systems, where downtime or rushed changes can have broad consequences. In systems that are difficult to update, the challenge is even more severe: not every flaw can be quickly corrected, and not every environment can safely absorb an immediate change.
The “smartification” of the economy has created new risks
Nadella’s remarks also highlighted an irony in the technology industry’s push to connect more devices and systems to the internet. The same “smartification” that has improved monitoring, efficiency and remote control has also expanded the number of entry points that attackers might exploit.
By connecting more of the world’s infrastructure to networks, organizations have gained visibility and flexibility. At the same time, they have inherited firmware issues, legacy systems and operational technology that were never built with today’s threat landscape in mind. Those weaknesses can be particularly troublesome when they sit inside systems that are expensive, delicate or impossible to take offline for extended maintenance.
Nadella pointed specifically to firmware, chillers and HVAC systems, emphasizing that these are not abstract risks. They are widely deployed components, and many are already connected to the internet. Once those devices are reachable, they become part of the same security surface as more familiar enterprise software.
Outages, latent bugs and the pressure on defenders
The conversation took place against the backdrop of a recent wave of large-scale outages, including one involving Microsoft Outlook. Other incidents have involved the NSA, the FAA and Apple. In those cases, concerns have circulated that cyberattacks may have been involved, although officials have denied those claims.
Nadella briefly addressed the Outlook disruption, describing it as the result of a “latent bug” that led to a “perfect storm.” He said Microsoft issued an incident response and would take the lessons from the event and apply them both upstream in architecture and in operations.
“We put out an incident response, and we’re going to obviously take all of the learnings, both upstream architectural, as well as operational, and fix that,” he said.
His comments suggest a familiar problem in modern software: systems can harbor latent flaws for long periods before conditions align to trigger a major failure. In a highly connected environment, a bug that would once have remained contained can ripple outward quickly and affect users around the world.
What makes critical infrastructure hard to secure
Nadella’s remarks point to several persistent challenges for organizations trying to secure critical infrastructure:
- Legacy firmware: Many devices rely on embedded code that is difficult to replace or update safely.
- Always-on systems: Transportation, cooling and other operational services often cannot be taken offline without disrupting essential functions.
- Internet exposure: As more devices connect to networks, the number of reachable targets grows.
- Rapid exploitation: AI can help attackers find and use flaws faster than defenders can react.
- Operational risk: Even a legitimate patch can introduce instability if deployed too quickly.
Those issues help explain why critical infrastructure security is often less about finding a single fix and more about managing risk over time. For many systems, modernization is necessary, but modernization is also slow, expensive and operationally complicated.
Modernization may be unavoidable, but it is not simple
Nadella said systems will need to be modernized and that organizations will have to assess what the threat landscape looks like and how well they can detect and defend in real time. That includes rethinking both the architecture of the systems themselves and the operational controls surrounding them.
“Somebody was telling me about sort of even the transportation systems and the amount of stuff that’s discoverable but with unpatchable firmware,” he said. “So we’ll have to really modernize for sure … and then we will have to assess what the threat vector looks like, what our own ability to both detect and then defend in real time looks like.”
The message was not that patching is obsolete, but that patching alone is no longer enough. In a world where vulnerabilities can be found and exploited quickly, organizations need better visibility, stronger segmentation, faster detection and more resilient recovery plans. For critical infrastructure, those capabilities may matter just as much as the patch itself.
For Microsoft, the remarks also underscored a tension facing major software companies: they must help secure a vast ecosystem they do not fully control, while also managing outages and bugs in their own products. Nadella’s comments framed that challenge as a systemic one, not just a Microsoft problem.
Source: Original report
Was this helpful?
Explore more: Application Audit & Review More Cybersecurity Tech News
Last Modified: November 19, 2026 at 10:33 pm
0 views