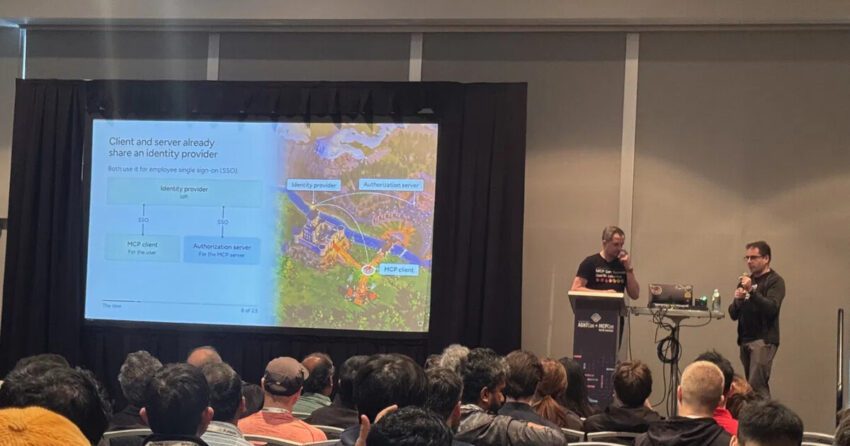
At AGNTCon + MCPCon North America 2026 in San Jose, the Agentic AI Foundation added four new projects, expanding from three founding projects to ten in its first year. The two-day event, held October 22-23 after the PyTorch Conference at the same venue, also signaled a clear shift in the MCP conversation: from feature growth toward security, identity, and trust.
Agentic AI Foundation expands with four additions
Mazin Gilbert, executive director of the Agentic AI Foundation (AAIF), opened the event with the project announcements and three new governance committees. The new additions came from four major players in the AI ecosystem, underscoring the foundation’s push to become a neutral home for agentic AI infrastructure.
- Alibaba contributed OpenSandbox, described as a secure sandbox for running agents.
- OpenAI contributed Open Responses, an open specification for interoperable LLM interfaces.
- Anthropic added Agent Skills.
- Hugging Face contributed OpenEnv, a framework for reinforcement learning environments used to train and evaluate agents.
Manik Surtani, the foundation’s CTO, framed the milestone simply: “A year ago, AAIF launched with three projects and a bet that agentic AI needed a neutral home to thrive. Today we host 10.”
MCP shifts from protocol features to security and identity
While the conference covered new protocol work, much of the program focused on the harder questions around identity, attestation, audit, and payments. Surtani argued in his talk, “Who Keeps It Open?”, that a license alone does not keep infrastructure open. He contrasted Android, which remained under one company, with Kubernetes, which Google moved into a neutral foundation.
That theme also surfaced in the MCP discussions. David Soria Parra, co-creator of MCP at Anthropic, said today’s capable models need connectivity more than help staying on task. He also pointed to the July 28 specification update, which added stateless servers. Some developers worry that could reduce MCP to “just another API,” but some platforms already see about 70% of their traffic in that mode.
Soria Parra also announced MCP tasks support in Claude Code, allowing tool calls to run for minutes, hours, or even days instead of seconds. Anthropic also donated the Agent Skills standard to the foundation. The project roadmap now lists five priority areas, spanning agent messaging, skills, MCP, identity, and an HTTP-native transport.
Security becomes the dominant concern
If previous MCP discussions centered on interoperability, this event made clear that security is now the urgent topic. Anthropic’s Den Delimarsky, the protocol’s lead maintainer, said cumulative SDK downloads have reached 4.17 billion, up from about 3 billion a month earlier. He said that growth raises the stakes of every security gap.
Delimarsky said about a third of the 116 conformance scenarios now test security, and that enterprise-managed authorization is live in Claude. His auth roadmap marks that feature as stable, places proof-of-possession tokens and workload identity federation in draft, and ends with agents that sign in as themselves.
OpenAI’s Thomas Sarlandie offered a practical look at what the ChatGPT plugin directory reveals about MCP servers in production. He said there is no practical limit on tool count, but oversized schemas get trimmed, starting with argument descriptions. About three in four tool schemas on published servers are under 1 kB, while the largest reach about 260 kB for a single tool and 1.4 MB for a server.
Sarlandie also said OpenAI rejects submitted servers unless every tool carries annotations, which let ChatGPT fast-track read-only calls and confirm destructive ones. Only 56% of plugins use server instructions, and he said those can safely run to about 1,000 characters.
Web standards, attack surfaces, and agent identity
Chrome’s Sarah Drasner introduced WebMCP, a proposed web standard now in origin trial that lets websites expose tools to agents. Rather than scraping the DOM, agents can call declared tools directly. Drasner cited benchmarks showing actions are 2.5 to 7.5 times faster, and said read-only and untrusted-content hints help agents resist prompt injection hidden in user comments.
Drasner emphasized that WebMCP complements MCP rather than replacing it. That distinction matters as more tooling moves into browser and web-facing workflows, where untrusted content can be a direct security risk.
Security concerns were echoed by Dawn Song, a UC Berkeley professor, who argued that frontier AI will help attackers more than defenders in the near term. She described CyberGym, a benchmark spanning more than 1,500 vulnerabilities across nearly 200 open source projects, and said models now find zero-days. On ExploitGym, she said GPT-5.6 Sol produced about 230 working exploits against 869 targets in two hours, and still more than 80 with standard security mitigations enabled.
Song called for secure-by-construction systems with AI-generated proofs and pointed to a new observatory tracking these capabilities. Her message was blunt: because attackers need only one hole, defenses must be built to reduce the entire attack surface.
Identity, review, and the economics of agent work
Identity surfaced repeatedly across the conference. Block’s Bradley Axen, creator of goose, demonstrated Buzz, an open source workspace where people and agents share channels. Each agent gets its own identity and an attestation naming its owner, and can read channels but not direct messages. Axen said Buzz has 80,000 communities and 36,000 GitHub stars, with version 1.0 due in mid-November.
Thomas Dohmke, former GitHub CEO and now CEO of Entire, argued that agents have shifted the bottleneck from coding to code review. He cited industry data showing teams using coding agents produce about 57 pull requests a week, compared with roughly 10 for others. Dohmke wants agent session logs stored in Git and linked to commits so reviewers can compare a change with its intent.
J.R. Storment, executive director of the 11-week-old Tokenomics Foundation, offered a more economic frame: stop counting tokens. He said cost per task beats cost per token, and cost per outcome is better still, but the true measure is business value.
Tim O’Reilly closed the broader philosophical loop by calling MCP an “architecture of participation” for AI, in the tradition of Unix. He argued that the AI economy still lacks the mechanisms it needs, much as the web needed pay-per-click advertising and secure payments. His prescription was mechanism design, or “reverse game theory”: define the desired outcome first, then work backward to the rules that produce it.
What developers should take away
For teams running MCP servers, the practical guidance from San Jose was straightforward. Annotate every tool, keep schemas small, and plan for agents that carry their own identity instead of relying only on borrowed user tokens. Several of the security extensions remain drafts, and some of the most ambitious numbers shared on stage were not backed by published data.
Even so, the event made one thing clear: the center of gravity around agentic AI is moving away from raw capability and toward the infrastructure needed to trust, audit, and safely operate it. The next AGNTCon + MCPCon events are set for San Francisco on April 28-29 and London on September 15-16, 2027.
Source: Original report
Was this helpful?
Explore more: Application Audit & Review More AI & Automation Tech News
Last Modified: October 27, 2026 at 10:33 pm
0 views